Encryption

Rare and Hardest To Crack Enigma Code Machine Sells For $437,000 (zdnet.com) 46

An anonymous reader writes: A rare 1944 four-rotor M4 Enigma cipher machine, considered one of the hardest challenges for the Allies to decrypt, has sold at a Christie's auction for $437,955. As noted by Christie's, the M4 Enigma has a special place in computing history as the Allied efforts to break its encryption led to the development of the first programmable computer, the one developed at Bletchley Park that was used to secretly break the M4, giving Allied forces visibility into German naval planning during the Battle of the Atlantic until its surrender in mid-1945.

The M4 Enigmas are considered rare because they were made in smaller numbers than three-rotor machines. After Germany capitulated, the country ordered troops to destroy remaining Enigmas in order to keep them from Allied forces. After the war Winston Churchill also ordered all remaining Enigmas destroyed to help preserve the secret of Allied decoding successes at Bletchley. The M4 Enigmas were made on the order of Admiral Karl Donitz, the commander of the German U-boat fleet, who had concerns over repeated Allied successes against his submarines. The M4 became available to the U-boat fleet in May 1941, preventing Allies from knowing where German's U-boats were positioned for almost a year until Turing and Joe Desch in Dayton, Ohio developed the computer that broke M4 encryption to decipher German messages. By mid-1943 the majority of M4 Enigma messages were being read by the Allies, but it was not until the 1970s that knowledge of the Allied successes against the Enigma was made public.
"Rival auction house Sotheby's sold an M4 Enigma last year for $800,000, which may have reached a higher selling price because it was one of one of 15 Enigma machines found in a bunker at Germany's key Northern European naval base in Trondheim, Norway, which Germany had occupied since 1940," adds ZDNet.
Chrome

Chrome 84 Arrives With SameSite Cookie Changes, Web OTP API and Web Animations API (venturebeat.com) 14

An anonymous reader quotes a report from VentureBeat: Google today launched Chrome 84 for Windows, Mac, Linux, Android, and iOS. Chrome 84 resumes SameSite cookie changes, includes the Web OTP API and Web Animations API, and removes older Transport Layer Security (TLS) versions. First deprecated with Chrome 81 in April, TLS 1.0 and TLS 1.1 have now been completely removed with Chrome 84. This is notable for anyone who manages a website, even if they don't use Chrome at home or at work. TLS is a cryptographic protocol designed to provide communications security over a computer network -- websites use it to secure all communications between their servers and browsers. TLS also succeeds Secure Sockets Layer (SSL) and thus handles the encryption of every HTTPS connection.

In May 2016, Chrome 51 introduced the SameSite attribute to allow sites to declare whether cookies should be restricted to a same-site (first-party) context. The hope was this would mitigate cross-site request forgeries (CSRF). Chrome 80 began enforcing a new secure-by-default cookie classification system, treating cookies that have no declared SameSite value as SameSite=Lax cookies. Only cookies set as SameSite=None; Secure are available in third-party contexts, provided they are being accessed from secure connections. Due to the coronavirus crisis, however, Google paused the SameSite cookie changes, with plans to resume enforcement sometime over the summer. SameSite cookie enforcement has now resumed with a gradual rollout ramping up over the next several weeks for Chrome 80 and newer.

Chrome 84 introduces the Web OTP API (formerly called the SMS Receiver API). This API helps users enter a one-time password (OTP) on a webpage when a specially crafted SMS message is delivered to their Android phone. When verifying the ownership of a phone number, developers typically send an OTP over SMS that must be manually entered by the user (or copied and pasted). The user has to switch to their native SMS app and back to their web app to input the code. The Web OTP API lets developers help users enter the code with one tap. Chrome 84 also adopts the Web Animations API, which gives developers more control over web animations. These can be used to help users navigate a digital space, remember your app or site, and provide implicit hints around how to use your product. Parts of the API have been around for some time, but this implementation brings greater spec compliance and supports compositing operations, which control how effects are combined and offer many new hooks that enable replaceable events. The API also supports Promises, which allow for animation sequencing and provide greater control over how animations interact with other app features.

Encryption

Enigma Code-Breaking Machine Rebuilt At Cambridge (techxplore.com) 34

Cambridge Engineering alumnus Hal Evans has built a fully-functioning replica of a 1930s Polish cyclometer -- an electromechanical cryptologic device that was designed to assist in the decryption of German Enigma ciphertext. The replica currently resides in King's College, Cambridge. TechXplore reports: Work on the hardware-based replica began in 2018, as part of Hal's fourth year Master's project under the supervision of King's College Fellow and Senior Tutor Dr. Tim Flack. The aim was to investigate further into cryptologist Marian Rejewski's cyclometer -- an early forerunner to Cambridge University mathematician Alan Turing's machine, known as the Bombe, which was used to crack the German Enigma code during the Second World War. Hal said he chose to work on the cyclometer as it was the very first machine used to assist the decryption effort. To his knowledge, the replica is the first fully-functioning hardware-based electromechanical cyclometer to exist since the years preceding the Second World War. The original machines would have been destroyed in 1939 to prevent them from falling into the hands of German invaders.

Rejewski's cyclometer exploited the German's procedure at the time of double encipherment of the Enigma message key, and semi-automated the process for calculating what were known as 'characteristics' for every possible Enigma rotor starting position. There were more than 100,000 of these rotor starting positions, and they each needed their characteristic to be calculated and catalogued in a card index system. The cyclometer therefore eliminated the arduous task of calculating these characteristics by hand. The machine consisted of, in effect, two interlinked Enigma systems side-by-side -- one offset by three positions relative to the other -- and 26 lamps and switches to cover the alphabet. On operation, a certain number of bulbs illuminated, indicating the lengths of the characteristics. These were recorded for every single possible rotor starting position to create an immense look-up catalogue. Once this was completed, obtaining the daily Enigma rotor starting settings to decode messages was a simple matter of intercepting enough messages and referencing the catalogue, taking only a matter of minutes.

Encryption

Signal's New PIN Feature Worries Cybersecurity Experts (vice.com) 45

Lorenzo Franceschi-Bicchierai, writing for Vice: Ever since NSA leaker Edward Snowden said "use Signal, use Tor," the end-to-end encrypted chat app has been a favorite of people who care about privacy and need a chat and calling app that is hard to spy on. One of the reasons security experts recommended Signal is because the app's developers collected -- and thus retained -- almost no information about its users. This means that, if subpoenaed by law enforcement, Signal would have essentially nothing to turn over. Signal demonstrated this in 2016, when it was subpoenaed by a court in Virginia. But a newly added feature that allows users to recover certain data, such as contacts, profile information, settings, and blocked users, has led some high-profile security experts to criticize the app's developers and threaten to stop using it.

Signal will store that data on servers the company owns, protected by a PIN that the app has initially been asking users to add, and then forced them to. The purpose of using a PIN is, in the near future, to allow Signal users to be identified by a username, as opposed to their phone number, as Signal founder Moxie Marlinspike explained on Twitter (as we've written before, this is a laudable goal; tying Signal to a phone number has its own privacy and security implications). But this also means that unlike in the past, Signal now retains certain user data, something that many cybersecurity and cryptography experts see as too dangerous. Matthew Green, a cryptographer and computer science professor at Johns Hopkins University, said that this was "the wrong decision," and that forcing users to create a PIN and use this feature would force him to stop using the app.

Businesses

Hackers Are Exploiting a 5-Alarm Bug In Networking Equipment (wired.com) 32

Andy Greenberg writes via Wired: Late last week, government agencies, including the United States Computer Emergency Readiness Team and Cyber Command, sounded the alarm about a particularly nasty vulnerability in a line of BIG-IP products sold by F5. The agencies recommended security professionals immediately implement a patch to protect the devices from hacking techniques that could fully take control of the networking equipment, offering access to all the traffic they touch and a foothold for deeper exploitation of any corporate network that uses them. Now some security companies say they're already seeing the F5 vulnerability being exploited in the wildâ"and they caution that any organization that didn't patch its F5 equipment over the weekend is already too late.

The F5 vulnerability, first discovered and disclosed to F5 by cybersecurity firm Positive Technologies, affects a series of so-called BIG-IP devices that act as load balancers within large enterprise networks, distributing traffic to different servers that host applications or websites. Positive Technologies found a so-called directory traversal bug in the web-based management interface for those BIG-IP devices, allowing anyone who can connect to them to access information they're not intended to. That vulnerability was exacerbated by another bug that allows an attacker to run a "shell" on the devices that essentially lets a hacker run any code on them that they choose. The result is that anyone who can find an internet-exposed, unpatched BIG-IP device can intercept and mess with any of the traffic it touches. Hackers could, for instance, intercept and redirect transactions made through a bank's website, or steal users' credentials. They could also use the hacked device as a hop point to try to compromise other devices on the network. Since BIG-IP devices have the ability to decrypt traffic bound for web servers, an attacker could even use the bug to steal the encryption keys that guarantee the security of an organization's HTTPS traffic with users, warns Kevin Gennuso, a cybersecurity practitioner for a major American retailer.
While only a small minority of F5 BIG-IP devices are directly exploitable, Positive Technologies says that still includes 8,000 devices worldwide. "About 40 percent of those are in the U.S., along with 16 percent in China and single-digit percentages in other countries around the globe," reports Wired.

"Owners of those devices have had since June 30, when F5 first revealed the bug along with its patch, to update," adds Wired. "But many may not have immediately realized the seriousness of the vulnerability. Others may have been hesitant to take their load balancing equipment offline to implement an untested patch, points out Gennuso, for fear that critical services might go down, which would further delay a fix."
Security

Body Cam with Military Police Footage Sold on Ebay (azmirror.com) 17

"A security researcher was able to access files on a Axon body-worn camera he purchased from eBay that had video files of Fort Huachuca Military Police officers conducting investigations and filling out paperwork," reports the Arizona Mirror: The files were able to be extracted after the researcher, who goes by KF on Twitter, was able to remove a microSD card from the body-worn camera. KF was then able to extract the un-encrypted files, which were not protected by a password, using a tool called Foremost. KF shared screenshots of the footage he was able to pull from the cards that appeared to show members of the Fort Huachuca Military Police entering a person's home and filling out paperwork.

"We are aware of this issue and have launched an investigation looking into the matter," a statement from Scottsdale-based Axon said to Arizona Mirror. "We are also reevaluating our processes to better emphasize proper disposal procedures for our customers."

The camera that was purchased by KF was an Axon Body 1, one of the company's earliest generation models that launched in 2013. The company said it stopped the model in 2015. "Our latest generation camera, Axon Body 3, offers enhanced security measures such as storage encryption to protect video from being retrieved from lost or improperly disposed cameras," the statement said.

Friday the original security researcher posted an update on Twitter, saying he'd offered to send the body cam's SD card back to the military police -- an offer that was eventually accepted by Axon itself -- and "I only listened to a few seconds of audio merely to verify its presence. I've since removed all extracted data in full."

In an earlier tweet he'd added, "Those of you asking... NO, I won't dump the card for you. Procure your own BWC (Body Worn Cam), and dump it yourself " But it looks like they already are. Earlier on Twitter, one Security Operations Center analyst posted, "I just ordered two myself.

"I'd actually really like to get a fund going to buy literally all of them and dump them to an open cloud storage bucket... Freedom of Information Act through the secondhand market."
The Media

US Senate Amends EARN IT Act -- To Let States Restrict Encryption (engadget.com) 89

Long-time Slashdot reader stikves reminded us that a committee in the U.S. Senate passed an amended version of the "EARN IT" act on Thursday. And this new version could do more than just end personal end-to-end encryption, warns Engadget: The other major concern opponents of the EARN IT Act raise has to do with Section 230 of the Communications Decency Act, which says that companies are not liable for much of the content that users post. Originally, the EARN IT Act proposed requiring that companies "earn" Section 230 protections by following recommended practices outlined by a Department of Justice commission. Without those protections, companies like Twitter or Facebook might be compelled to remove anything that might prompt a legal challenge, which could threaten freedom of speech. The amendments passed Thursday strip the Department of Justice commission of any legal authority and will not require companies to earn Section 230 protections by following recommended practices.

But the amended bill would change Section 230 to allow lawsuits from states, and state legislatures could restrict or outlaw encryption technologies.

The senior policy counsel for Free Press Action, a media reform advocacy group, harshly criticized the legislation's new version.

"Even as amended today, it invites states to begin passing all sorts of laws under the guise of protecting against abuse, but replicating the problems with the original EARN IT Act's text."
Encryption

Inside the Plot To Kill the Open Technology Fund (vice.com) 80

An anonymous reader quotes a report from VICE News: [The Open Technology Fund is a U.S. government-funded nonprofit, which is part of the umbrella group called the U.S. Agency for Global Media (USAGM), which also controls Radio Free Asia and Voice of America.] OTF's goal is to help oppressed communities across the globe by building the digital tools they need and offering training and support to use those tools. Its work has saved countless lives, and every single day millions of people use OTF-assisted tools to communicate and speak out without fear of arrest, retribution, or even death. The fund has helped dissidents raise their voices beyond China's advanced censorship network, known as the Great Firewall; helped citizens in Cuba to access news from sources other than the state-sanctioned media; and supported independent journalists in Russia so they could work without fear of a backlash from the Kremlin. Closer to home, the tools that OTF has funded, including the encrypted messaging app Signal, have allowed Black Lives Matter protesters to organize demonstrations across the country more securely.

But now all of that is under threat, after Michael Pack, a Trump appointee and close ally of Steve Bannon, took control of USAGM in June. Pack has ousted the OTF's leadership, removed its bipartisan board, and replaced it with Trump loyalists, including Bethany Kozma, an anti-transgender activist. One reason the OTF managed to gain the trust of technologists and activists around the world is because, as its name suggests, it invested largely in open-source technology. By definition, open-source software's source code is publicly available, meaning it can be studied, vetted, and in many cases contributed to by anyone in the world. This transparency makes it possible for experts to study code to see if it has, for example, backdoors or vulnerabilities that would allow for governments to compromise the software's security, potentially putting users at risk of being surveilled or identified. Now, groups linked to Pack and Bannon have been pressing for the funding of closed-source technology, which is antithetical to the OTF's work over the last eight years.
Pack is being pressed to fund Freegate and Ultrasurf, "two little-known apps that allow users to circumvent internet censorship in repressive regimes but currently have very small user bases inside China," reports Vice. "These apps are not widely trusted by internet freedom experts and activists, according to six experts who spoke to VICE News. That the OTF would pivot its funding from trusted, open-source tech to more obscure, closed-source tech has alarmed activists around the world and has resulted in open revolt among OTF's former leadership."

More than half a dozen experts who spoke to VICE News "said the apps' code is out of date, dangerously vulnerable to compromise, and lacks the user base to allow it to effectively scale even if they secured government funding."
Privacy

Journalist's Phone Hacked: All He Had To Do Was Visit a Website. Any Website. (thestar.com) 123

The iPhone that Moroccan journalist Omar Radi used to contact his sources also allowed his government to spy on him (and at least two other journalists), reports the Toronto Star, citing new research from Amnesty International.

A Slashdot reader shares their report: Their government could read every email, text and website visited; listen to every phone call and watch every video conference; download calendar entries, monitor GPS coordinates, and even turn on the camera and microphone to see and hear where the phone was at any moment.

Yet Radi was trained in encryption and cyber security. He hadn't clicked on any suspicious links and didn't have any missed calls on WhatsApp — both well-documented ways a cell phone can be hacked. Instead, a report published Monday by Amnesty International shows Radi was targeted by a new and frighteningly stealthy technique. All he had to do was visit one website. Any website.

Forensic evidence gathered by Amnesty International on Radi's phone shows that it was infected by "network injection," a fully automated method where an attacker intercepts a cellular signal when it makes a request to visit a website. In milliseconds, the web browser is diverted to a malicious site and spyware code is downloaded that allows remote access to everything on the phone. The browser then redirects to the intended website and the user is none the wiser.

Two more human rights advocates in Morocco have been targeted by the same malware, the article reports.
Encryption

Apple, Microsoft, Facebook, Google, Twitter, and Other Major Tech Companies Decry Republican Bill Seeking To Break Encryption (medianama.com) 66

In response to the Lawful Access to Encrypted Data (LAED) Act proposed by three Republican senators, Big Tech companies have registered their opposition through their Reform Government Surveillance coalition. From a report: They said that building encryption backdoors would jeopardize the sensitive data of billions of users and "leave all Americans, businesses, and government agencies dangerously exposed to cyber threats from criminals and foreign adversaries." They also pointed out that as the pandemic has forced everyone to rely on the internet "in critical ways," digital security is paramount and strong encryption is the way forward. The coalition's members are Apple, Microsoft, Facebook, Google, Twitter, Snap, Verizon Media, Dropbox, and Microsoft-owned LinkedIn. The coalition was established in December 2013, a few months after documents about the United States' PRISM data collection program were leaked.
Mozilla

Comcast Becomes the First ISP To Join Mozilla's TRR Program (neowin.net) 85

Comcast has joined Cloudflare and NextDNS in partnering with Mozilla's Trusted Recursive Resolver program, which aims to make DNS more trusted and secure. Neowin reports: Commenting on the move, Firefox CTO Eric Rescorla, said: "Comcast has moved quickly to adopt DNS encryption technology and we're excited to have them join the TRR program. Bringing ISPs into the TRR program helps us protect user privacy online without disrupting existing user experiences. We hope this sets a precedent for further cooperation between browsers and ISPs."

With its TRR program, Mozilla said that encrypting DNS data with DoH is just the first step in securing DNS. It said that the second step requires companies handling the data to have appropriate rules in place for handling it. Mozilla believes these rules include limiting data collection and retention, ensuring transparency about any retained data, and limiting the use of the resolver to block access or modify content.
Ars Technica notes that joining Mozilla's program means that Comcast agreed that it won't "retain, sell, or transfer to any third party (except as may be required by law) any personal information, IP addresses, or other user identifiers, or user query patterns from the DNS queries sent from the Firefox browser," along with other requirements.

When the change happens, it'll be automatic for users unless they've chosen a different DoH provider or disabled DoH altogether. Comcast told Ars yesterday that "Firefox users on Xfinity should automatically default to Xfinity resolvers under Mozilla's Trusted Recursive Resolver program, unless they have manually chosen a different resolver, or if DoH is disabled. The precise mechanism is still being tested and the companies plan to document it soon in an IETF [Internet Engineering Task Force] Draft."
Republicans

Republicans Push Bill Requiring Tech Companies To Help Access Encrypted Data (cnet.com) 182

New submitter feross shares a report: A group of Senate Republicans is looking to force tech companies to comply with "lawful access" to encrypted information, potentially jeopardizing the technology's security features. On Tuesday, Republican lawmakers introduced the Lawful Access to Encrypted Data Act, which calls for an end to "warrant-proof" encryption that's disrupted criminal investigations. The bill was proposed by Sen. Lindsey Graham, chairman of the Senate Judiciary committee, along with Sens. Tom Cotton and Marsha Blackburn. If passed, the act would require tech companies to help investigators access encrypted data if that assistance would help carry out a warrant. Lawmakers and the US Justice Department have long battled with tech companies over encryption, which is used to encode data.

The Justice Department argues that encryption prevents investigators from getting necessary evidence from suspects' devices and has requested that tech giants provide "lawful access." That could come in many ways, such as providing a key to unlock encryption that's only available for police requests. The FBI made a similar request to Apple in 2016 when it wanted to get data from a dead terrorist's iPhone in a San Bernardino, California, shooting case. Giving access specifically to government agencies when requested is often referred to as an "encryption backdoor," something tech experts and privacy advocates have long argued endangers more people than it helps.

Printer

80,000 Printers Are Exposing Their IPP Port Online (zdnet.com) 56

An anonymous reader quotes a report from ZDNet: In a report published earlier this month, security researchers from the Shadowserver Foundation, a non-profit organization focused on improving cyber-security practices across the world, have published a warning about companies that are leaving printers exposed online. More specifically, Shadowserver experts scanned all the four billion routable IPv4 addresses for printers that are exposing their IPP port. IPP stands for "Internet Printing Protocol" and, as the name suggests, is a protocol that allows users to manage internet-connected printers and send printing jobs to printers hosted online. The difference between IPP and the multiple other printer management protocols is that IPP is a secure protocol that supports advanced features such as access control lists, authentication, and encrypted communications. However, this doesn't mean that device owners are making use of any of these features.

Shadowserver experts said they specifically scanned the internet for IPP-capable printers that were left exposed without being protected by a firewall and allowed attackers to query for local details via the "Get-Printer-Attributes" function. In total, experts said they usually found an average of around 80,000 printers exposing themselves online via the IPP port on a daily basis. The number is about an eighth of all IPP-capable printers currently connected online. A normal scan with the BinaryEdge search engine reveals a daily count of between 650,000 and 700,000 devices with their IPP port (TCP/631) reachable via the internet.
What are the issues with not securing the IPP port? Shadowserver experts say this port can be used for intelligence gathering, since many of the printers scanned returned additional info about themselves, such as printer names, locations, models, firmware, organization names, and even Wi-Fi network names.

"To configure IPP access control and IPP authentication features, users are advised to check their printers' manuals," adds ZDNet. "Most printers have an IPP configuration section in their administration panel from where users can enable authentication, encryption, and limit access to the device via access lists."
Businesses

Encrypted Phone Network Says It's Shutting Down After Police Hack (vice.com) 31

Someone in control of an email address long associated with Encrochat, a company that sells custom encrypted phones often used by organized criminals, tells Motherboard the company is shutting down after a law enforcement hacking operation against its customers. From a report: The news comes as law enforcement agencies have arrested multiple criminal users of Encrochat across Europe in what appears to be a large scale, coordinated operation against the phone network and its users. "We have been forced to make the difficult decision to shut down our service and our business permanently," the person wrote in an email to Motherboard. "This [sic] following several attacks carried out by a foreign organization that seems to originate in the UK." The email address has been linked to Encrochat for years, but Motherboard could not confirm the identity of the person currently using the account. Motherboard also separately obtained screenshots of text messages sent over the past week of alleged Encrochat users discussing a wave of arrests associated with the Encrochat takeover. Encrochat is part of the encrypted phone industry, which sells devices pre-loaded with private messaging apps, sometimes have the GPS or camera functionality physically removed, and can be remotely wiped by the user.
Piracy

Discord Removes Servers Dedicated To Pirating Porn (vice.com) 46

After Motherboard discovered multiple servers on Discord containing pirated porn, the chat platform removed them and banned the owners of each. From a report: "Discord prohibits the sale, dissemination, and promotion of cracked accounts," a spokesperson told Motherboard. "We ban users and shut down servers that are responsible for this behavior. In cases of copyrighted material, we respond promptly to DMCA takedown requests and take the appropriate action." The bans are permanent, and the owners can no longer access their accounts for any purpose. Former members of those servers can no longer access those servers, either.

During Motherboard's reporting, Google removed an OnlyFans scraping Chrome extension when approached for comment. Stolen content is a problem that has plagued the adult industry for as long as porn has existed on the internet. Several owners of premium platforms similar to OnlyFans urged the industry to do better in how it safeguards content, by protecting models from theft using more advanced fingerprinting, watermarking, copyright takedown support, and technology that could prevent scrapers from using these tools to begin with.

Privacy

Zoom To Launch End-to-End Encryption For All Users -- Not Just Paid Accounts (blog.zoom.us) 39

Weeks after Zoom said it will offer end-to-end encryption to only paying customers -- a move that was received poorly by several privacy and security advocates, the popular video calling software said on Wednesday it is making some amendments: We are also pleased to share that we have identified a path forward that balances the legitimate right of all users to privacy and the safety of users on our platform. This will enable us to offer E2EE (end-to-end encryption) as an advanced add-on feature for all of our users around the globe -- free and paid -- while maintaining the ability to prevent and fight abuse on our platform. To make this possible, Free/Basic users seeking access to E2EE will participate in a one-time process that will prompt the user for additional pieces of information, such as verifying a phone number via a text message. Many leading companies perform similar steps on account creation to reduce the mass creation of abusive accounts. We are confident that by implementing risk-based authentication, in combination with our current mix of tools -- including our Report a User function -- we can continue to prevent and fight abuse.
Mozilla

Mozilla, EFF, 19,000 Citizens Urge Zoom To Reverse End-to-End Encryption Decision 44

Mozilla, Electronic Frontier Foundation (EFF), and more than 19,000 internet users today urged Zoom CEO Eric Yuan to reverse his decision to deny end-to-end encryption to users of its free service end-to-end encryption, saying it puts activists and other marginalized groups at risk. Earlier this month, Zoom announced it will offer end-to-end encryption, but only to those who pay. From a statement: The pressure to reverse the decision comes as racial justice activists are using tools like Zoom to organize protests. Without end-to-end encryption, information shared in their online meetings could be intercepted -- a concern that has been legitimized by both recent actions by law enforcement and a long-term history of discriminatory policing. Mozilla and EFF today are presenting an open letter to Yuan, co-signed by 19,000 people, maintaining that privacy and best-in-class security should be the default, not something that only the wealthy or businesses can afford.
The Almighty Buck

South African Bank To Replace 12 Million Cards After Employees Stole Master Key (theverge.com) 36

Postbank, the banking division of South Africa's Post Office, has lost more than $3.2 million from fraudulent transactions and will now have to replace more than 12 million cards for its customers after employees printed and then stole its master key. ZDNet reports: The Sunday Times of South Africa, the local news outlet that broke the story, said the incident took place in December 2018 when someone printed the bank's master key on a piece of paper at its old data center in the city of Pretoria. The bank suspects that employees are behind the breach, the news publication said, citing an internal security audit they obtained from a source in the bank.

The master key is a 36-digit code (encryption key) that allows its holder to decrypt the bank's operations and even access and modify banking systems. It is also used to generate keys for customer cards. The internal report said that between March and December 2019, the rogue employees used the master key to access accounts and make more than 25,000 fraudulent transactions, stealing more than $3.2 million (56 million rand) from customer balances. Following the discovery of the breach, Postbank will now have to replace all customer cards that have been generated with the master key, an operation the bank suspects it would cost it more than one billion rands (~$58 million). This includes replacing normal payment cards, but also cards for receiving government social benefits. Sunday Times said that roughly eight to ten million of the cards are for receiving social grants, and these were where most of the fraudulent operations had taken place.

Privacy

How Accurate Were Ray Kurzweil's Predictions for 2019? (lesswrong.com) 70

In 1999, Ray Kurzweil made predictions about what the world would be like 20 years in the future. Last month the community blog LessWrong took a look at how accurate Kurzweil's predictions turned out to be: This was a follow up to a previous assessment about his predictions about 2009, which showed a mixed bag, roughly evenly divided between right and wrong, which I'd found pretty good for 10-year predictions... For the 2019 predictions, I divided them into 105 separate statements, did a call for volunteers [and] got 46 volunteers with valid email addresses, of which 34 returned their predictions... Of the 34 assessors, 24 went the whole hog and did all 105 predictions; on average, 91 predictions were assessed by each person, a total of 3078 individual assessments...

Kurzweil's predictions for 2019 were considerably worse than those for 2009, with more than half strongly wrong.

The assessors ultimately categorized just 12% of Kurzweil's predictions as true, with another 12% declared "weakly true," while another 10% were classed as "cannot decide." But 52% were declared "false" -- with another 15% also called "weakly false."

Among Kurzweil's false predictions for the year 2019:
  • "Phone" calls routinely include high-resolution three-dimensional images projected through the direct-eye displays and auditory lenses... Thus a person can be fooled as to whether or not another person is physically present or is being projected through electronic communication.
  • The all-enveloping tactile environment is now widely available and fully convincing.

"As you can see, Kurzweil suffered a lot from his VR predictions," explains the LessWrong blogpost. "This seems a perennial thing: Hollywood is always convinced that mass 3D is just around the corner; technologists are convinced that VR is imminent."

But the blog post also thanks Kurzweil, "who, unlike most prognosticators, had the guts and the courtesy to write down his predictions and give them a date. I strongly suspect that most people's 1999 predictions about 2019 would have been a lot worse."

And they also took special note of Kurzweil's two most accurate predictions. First, "The existence of the human underclass continues as an issue." And second:

"People attempt to protect their privacy with near-unbreakable encryption technologies, but privacy continues to be a major political and social issue with each individual's practically every move stored in a database somewhere."


Programming

GitHub, Android, Python, Go: More Software Adopts Race-Neutral Terminology (zdnet.com) 413

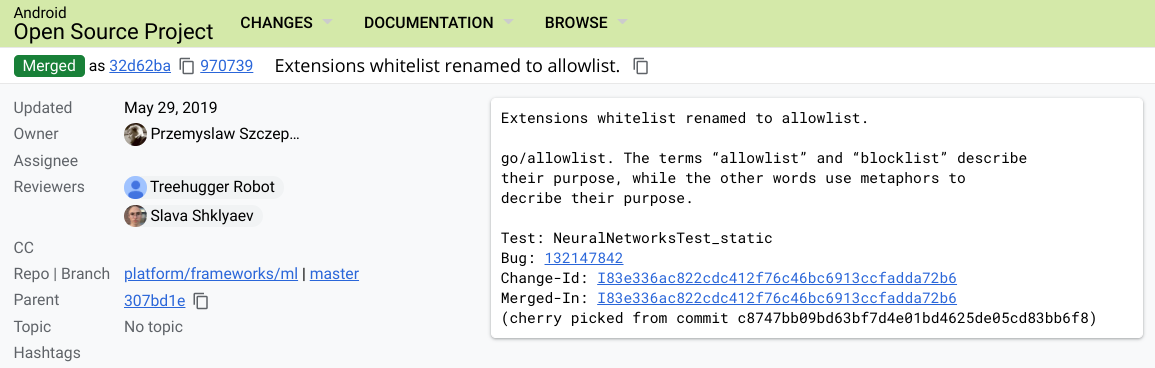
"The terms 'allowlist' and 'blocklist' describe their purpose, while the other words use metaphors to describe their purpose," reads a change description on the source code for Android -- from over a year ago. 9to5Mac calls it "a shortened version of Google's (internal-only) explanation" for terminology changes which are now becoming more widespread.

And Thursday GitHub's CEO said they were also "already working on" renaming the default branches of code from "master" to a more neutral term like "main," reports ZDNet: GitHub lending its backing to this movement effectively ensures the term will be removed across millions of projects, and effectively legitimizes the effort to clean up software terminology that started this month.

But, in reality, these efforts started years ago, in 2014, when the Drupal project first moved in to replace "master/slave" terminology with "primary/replica." Drupal's move was followed by the Python programming language, Chromium (the open source browser project at the base of Chrome), Microsoft's Roslyn .NET compiler, and the PostgreSQL and Redis database systems... The PHPUnit library and the Curl file download utility have stated their intention to replace blacklist/whitelist with neutral alternatives. Similarly, the OpenZFS file storage manager has also replaced its master/slave terms used for describing relations between storage environments with suitable replacements. Gabriel Csapo, a software engineer at LinkedIn, said on Twitter this week that he's also in the process of filing requests to update many of Microsoft's internal libraries.

A recent change description for the Go programming language says "There's been plenty of discussion on the usage of these terms in tech. I'm not trying to have yet another debate." It's clear that there are people who are hurt by them and who are made to feel unwelcome by their use due not to technical reasons but to their historical and social context. That's simply enough reason to replace them.

Anyway, allowlist and blocklist are more self-explanatory than whitelist and blacklist, so this change has negative cost.

That change was merged on June 9th -- but 9to5Mac reports it's just one of many places these changes are happening. "The Chrome team is beginning to eliminate even subtle forms of racism by moving away from terms like 'blacklist' and 'whitelist.' Google's Android team is now implementing a similar effort to replace the words 'blacklist' and 'whitelist.'" And ZDNet reports more open source projects are working on changing the name of their default Git repo from "master" to alternatives like main, default, primary, root, or another, including the OpenSSL encryption software library, automation software Ansible, Microsoft's PowerShell scripting language, the P5.js JavaScript library, and many others.

Slashdot Top Deals