Transportation

Texas Sues Allstate For Collecting Driver Data To Raise Premiums (gizmodo.com) 62

An anonymous reader quotes a report from Gizmodo: Texas has sued (PDF) one of the nation's largest car insurance providers alleging that it violated the state's privacy laws by surreptitiously collecting detailed location data on millions of drivers and using that information to justify raising insurance premiums. The state's attorney general, Ken Paxton, said the lawsuit against Allstate and its subsidiary Arity is the first enforcement action ever filed by a state attorney general to enforce a data privacy law. It also follows a deceptive business practice lawsuit he filed against General Motors accusing the car manufacturer of misleading customers by collecting and selling driver data.

In 2015, Allstate developed the Arity Driving Engine software development kit (SDK), a package of code that the company allegedly paid mobile app developers to install in their products in order to collect a variety of sensitive data from consumers' phones. The SDK gathered phone geolocation data, accelerometer, and gyroscopic data, details about where phone owners started and ended their trips, and information about "driving behavior," such as whether phone owners appeared to be speeding or driving while distracted, according to the lawsuit. The apps that installed the SDK included GasBuddy, Fuel Rewards, and Life360, a popular family monitoring app, according to the lawsuit.

Paxton's complaint said that Allstate and Arity used the data collected by its SDK to develop and sell products to other insurers like Drivesight, an algorithmic model that assigned a driving risk score to individuals, and ArityIQ, which allowed other insurers to "[a]ccess actual driving behavior collected from mobile phones and connected vehicles to use at time of quote to more precisely price nearly any driver." Allstate and Arity marketed the products as providing "driver behavior" data but because the information was collected via mobile phones the companies had no way of determining whether the owner was actually driving, according to the lawsuit. "For example, if a person was a passenger in a bus, a taxi, or in a friend's car, and that vehicle's driver sped, hard braked, or made a sharp turn, Defendants would conclude that the passenger, not the actual driver, engaged in 'bad' driving behavior," the suit states. Neither Allstate and Arity nor the app developers properly informed customers in their privacy policies about what data the SDK was collecting or how it would be used, according to the lawsuit.
The lawsuit violates Texas' Data Privacy and Security Act (DPSA) and insurance code by failing to address violations within the required 30-day cure period. "In its complaint, filed in federal court, Texas requested that Allstate be ordered to pay a penalty of $7,500 per violation of the state's data privacy law and $10,000 per violation of the state's insurance code, which would likely amount to millions of dollars given the number of consumers allegedly affected," adds the report.

"The lawsuit also asks the court to make Allstate delete all the data it obtained through actions that allegedly violated the privacy law and to make full restitution to customers harmed by the companies' actions."
Earth

Supreme Court Allows Hawaii To Sue Oil Companies Over Climate Change Effects (cbsnews.com) 75

An anonymous reader quotes a report from CBS News: The Supreme Court on Monday said it will not consider whether to quash lawsuits brought by Honolulu seeking billions of dollars from oil and gas companies for the damage caused by the effects of climate change, clearing the way for the cases to move forward. The legal battle pursued in Hawaii state court is similar to others filed against the nation's largest energy companies by state and local governments in their courts. The suits claim that the oil and gas industry engaged in a deceptive campaign and misled the public about the dangers of their fossil fuel products and the environmental impacts.

A group of 15 energy companies asked the Supreme Court to review a decision from the Hawaii Supreme Court that allowed a lawsuit brought by the city and county of Honolulu, as well as its Board of Water Supply, to proceed. The suit was brought in Hawaii state court in March 2020, and Honolulu raised (PDF) several claims under state law, including creating a public nuisance and failure to warn the public of the risks posed by their fossil fuel products. The city accused the oil and gas industry of contributing to global climate change, leading to flooding, erosion and more frequent and intense extreme weather events. These changes, they said, have led to property damage and a drop in tax revenue as a result of less tourism.

The energy companies unsuccessfully sought to have the case moved to federal court, arguing that the claims raised by Honolulu under state law were overridden by federal law and the Clean Air Act. A state trial court denied their efforts to dismiss the case. The oil and gas industry has argued that greenhouse-gas emissions "flow from billions of daily choices, over more than a century, by governments, companies and individuals about what types of fuels to use, and how to use them." Honolulu, the companies said, was seeking damages for the "cumulative effect of worldwide emissions leading to global climate change." The Hawaii Supreme Court ultimately allowed (PDF) the lawsuit to proceed. The state's highest court determined that the Clean Air Act displaced federal common law governing suits seeking damages for interstate pollution. It also rejected the oil companies' argument that Honolulu was seeking to regulate emissions through its lawsuit, finding that the city instead wanted to challenge the promotion and sale of fossil fuel products "without warning and abetted by a sophisticated disinformation campaign."

"Plaintiffs' state tort law claims do not seek to regulate emissions, and there is thus no 'actual conflict' between Hawaii tort law and the [Clean Air Act]," the Hawaii Supreme Court ruled. "These claims potentially regulate marketing conduct while the CAA regulates pollution." The oil companies asked the U.S. Supreme Court to review the ruling from the Hawaii high court and urged it to stop Honolulu's lawsuit from going forward. Regulation of interstate pollution is a federal area governed by federal law, lawyers for the energy industry argued. [...] The Supreme Court in June asked the Biden administration to weigh in on the cases and whether it should step into the dispute. In a filing submitted to the Supreme Court before the transfer of presidential power, the Biden administration urged the justices to turn away the appeals, in part because it said it is too soon for them to intervene.

The Internet

New York Starts Enforcing $15 Broadband Law That ISPs Tried To Kill (arstechnica.com) 32

Ars Technica's Jon Brodkin reports: The New York law requiring Internet providers to offer cheap plans to people with low incomes will take effect on Wednesday this week following a multi-year court battle in which the state defeated broadband industry lobby groups. A US appeals court upheld the law in April 2024, reversing the ruling of a district judge who blocked it in 2021. The Supreme Court last month decided not to hear the broadband industry's challenge, leaving the appeals court ruling in place. The state law requires Internet providers to offer $15- or $20-per-month service to people with low incomes.

As we've written, the battle between New York and ISPs was an important test case for how states can regulate broadband providers when the Federal Communications Commission isn't doing so. The Biden-era FCC's attempt to reinstate net neutrality rules and regulate broadband providers as common carriers was blocked in court, but ISPs lost the fight against the New York affordability law and an earlier fight against California's net neutrality law.

New York-based ISPs can comply by offering $15 broadband plans with download speeds of at least 25Mbps, or $20-per-month service with 200Mbps speeds. The price must include "any recurring taxes and fees such as recurring rental fees for service provider equipment required to obtain broadband service and usage fees." Price increases are to be capped at 2 percent per year, and state officials will periodically review whether minimum required speeds should be raised. New York Public Service Commission Chair Rory Christian last week issued an order stating that the law will take effect on January 15.
"On December 16, 2024, the United States Supreme Court denied the Plaintiff's request for further review," the order said. "As part of the litigation, the [New York attorney general] agreed not to enforce the ABA [Affordable Broadband Act] until 30 days after the date when the US Supreme Court decided the writ of Certiorari. Thus, the ABA will once again take effect and may be enforced in New York on January 15, 2025." The order said it plans to implement the law quickly because of "developments at the federal level impacting the affordability of broadband service."

ISPs can receive one-month exemptions by filing paperwork by Wednesday confirming they meet the subscriber threshold, notes Ars. To secure longer-term exemptions, ISPs must submit detailed financial information by February 15.
Oracle

Oracle Won't Withdraw 'JavaScript' Trademark, Says Deno. Legal Skirmish Continues (infoworld.com) 68

"Oracle has informed us they won't voluntarily withdraw their trademark on 'JavaScript'." That's the word coming from the company behind Deno, the alternative JavaScript/TypeScript/WebAssembly runtime, which is pursuing a formal cancellation with the U.S. Patent and Trademark Office.

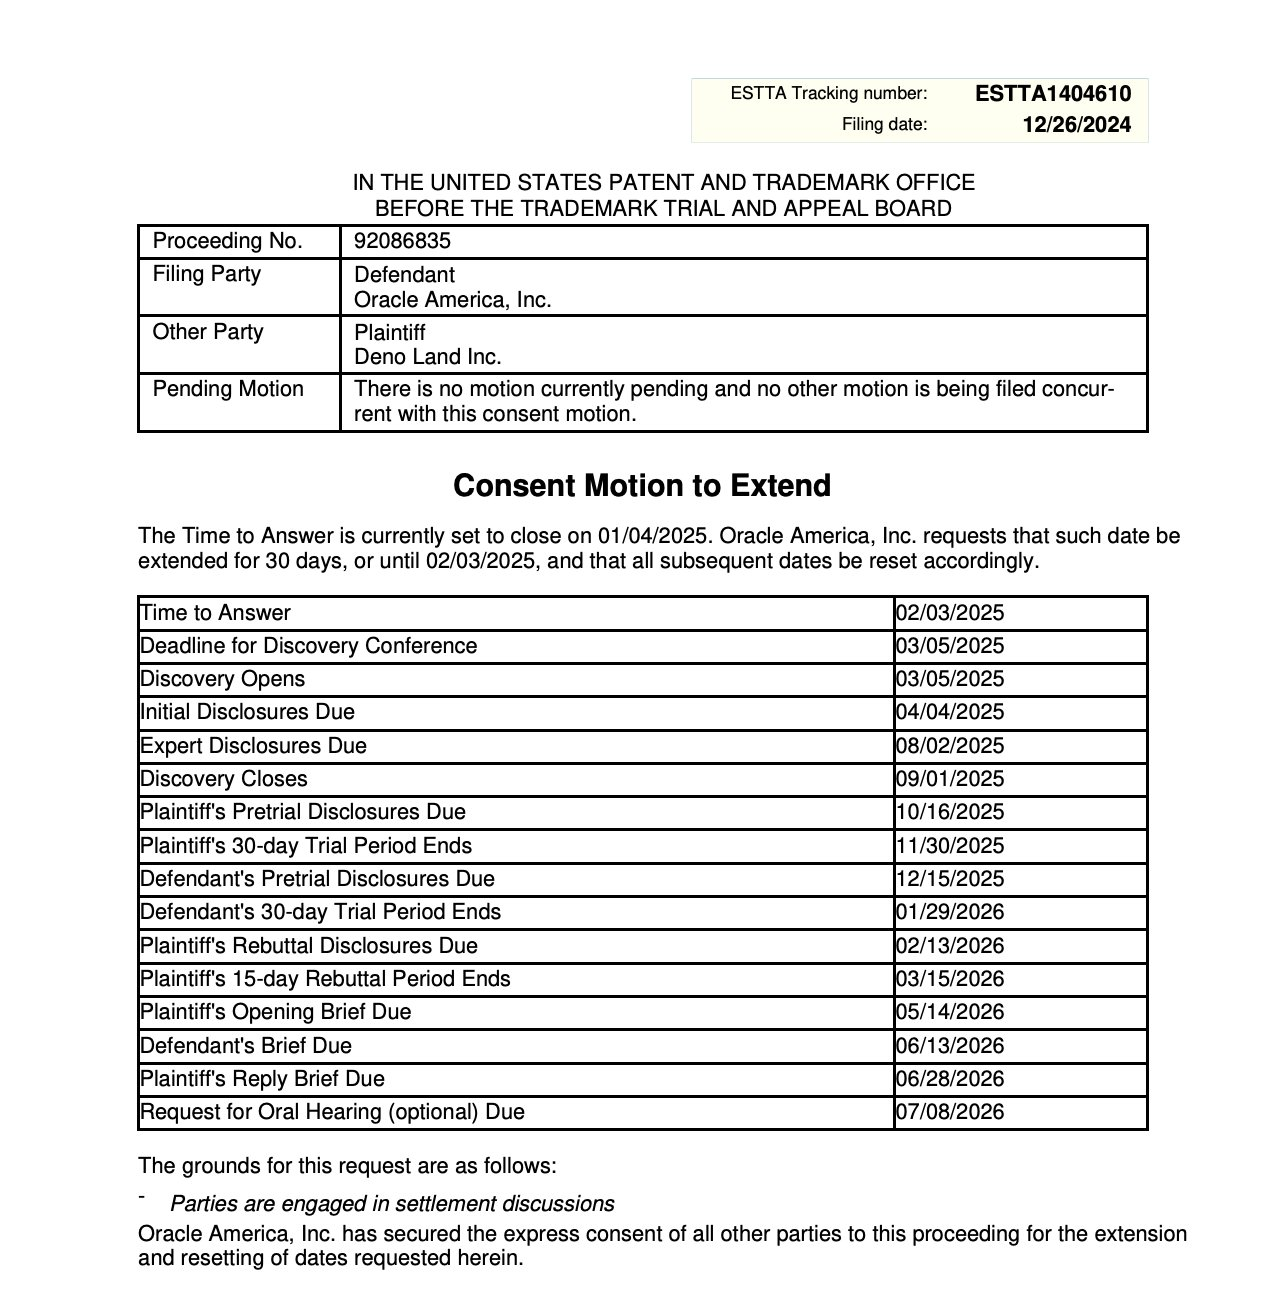
So what happens next? Oracle "will file their Answer, and we'll start discovery to show how 'JavaScript' is widely recognized as a generic term and not controlled by Oracle." Deno's social media posts show a schedule of various court dates that extend through July of 2026, so "The dispute between Oracle and Deno Land could go on for quite a while," reports InfoWorld: Deno Land co-founder Ryan Dahl, creator of both the Deno and Node.js runtimes, said a formal answer from Oracle is expected before February 3, unless Oracle extends the deadline again. "After that, we will begin the process of discovery, which is where the real legal work begins. It will be interesting to see how Oracle argues against our claims — genericide, fraud on the USPTO, and non-use of the mark."

The legal process begins with a discovery conference by March 5, with discovery closing by September 1, followed by pretrial disclosure from October 16 to December 15. An optional request for an oral hearing is due by July 8, 2026.

Oracle took ownership of JavaScript's trademark in 2009 when it purchased Sun Microsystems, InfoWorld notes.

But "Oracle does not control (and has never controlled) any aspect of the specification or how the phrase 'JavaScript' can be used by others," argues an official petition filed by Deno Land Inc. with the United States Patent and Trademark Office: Today, millions of companies, universities, academics, and programmers, including Petitioner, use "JavaScript" daily without any involvement with Oracle. The phrase "JavaScript" does not belong to one corporation. It belongs to the public. JavaScript is the generic name for one of the bedrock languages of modern programming, and, therefore, the Registered Mark must be canceled.

An open letter to Oracle discussing the genericness of the phrase "JavaScript," published at https://javascript.tm/, was signed by 14,000+ individuals at the time of this Petition to Cancel, including notable figures such as Brendan Eich, the creator of JavaScript, and the current editors of the JavaScript specification, Michael Ficarra and Shu-yu Guo. There is broad industry and public consensus that the term "JavaScript" is generic.

The seven-page petition goes into great detail, reports InfoWorld. "Deno Land also accused Oracle of committing fraud in its trademark renewal efforts in 2019 by submitting screen captures of the website of JavaScript runtime Node.js, even though Node.js was not affiliated with Oracle."
Earth

California's Wildfires Still Burn. Prison Inmates Join the Fight (npr.org) 101

As an ecological disaster devastated two coastal California cities, more than 7,500 firefighters pushed back against the wildfires. 900 of them are inmates, reports NPR. That's about 12%: California is one of more than a dozen states that operates conservation camps, commonly known as fire camps, for incarcerated people to train to fight fires and respond to other disasters... There are now 35 such camps in California, all of which are minimum-security facilities... When they are not fighting fires, they also respond to floods and other disasters and emergencies. Otherwise, the crews do community service work in areas close to their camp, according to the state corrections department...

A 2018 Time investigation found that incarcerated firefighters are at a higher risk for serious injuries. They also are more than four times as likely to get cuts, bruises or broken bones compared to professional firefighters working the same fires, the report found. They were also more than eight times as likely to face injuries after inhaling smoke, ash and other debris compared with other firefighters, the report said.

"Two of the camps are for incarcerated women," reports the BBC. One of them — since released — remembers that "It felt like you were doing something that mattered instead of rotting away in a cell," according to the nonprofit new site CalMatters. They can also earn credits that help reduce their prison sentences, the BBC learned from the California Department of Corrections and Rehabilitation.

Friday one local California news report shared the perspective of formerly incarcerated Californian, Matthew Hahn (from a 2021 Washington Post column). "Yes, the decision to take part is largely made under duress, given the alternative. Yes, incarcerated firefighters are paid pennies for an invaluable task. And yes, it is difficult though not impossible for participants to become firefighters after leaving prison," Hahn said. "Despite this, fire camps remain the most humane places to do time in the California prison system."
From that 2021 Washington Post column: California prisons have, on average, three times the murder rate of the country overall and twice the rate of all American prisons. These figures don't take into account the sheer number of physical assaults that occur behind prison walls. Prison feels like a dangerous place because it is. Whether it's individual assaults or large-scale riots, the potential for violence is ever-present. Fire camp represents a reprieve from that risk. Sure, people can die in fire camp as well — at least three convict-firefighters have died working to contain fires in California since 2017 — but the threat doesn't weigh on the mind like the prospect of being murdered by a fellow prisoner. I will never forget the relief I felt the day I set foot in a fire camp in Los Angeles County, like an enormous burden had been lifted...

[When his 12-man crew was called to fight the Jesusita Fire], the fire had ignited one home's deck and was slowly burning its way to the structure. We cut the deck off the house, saving the home. I often fantasize about the owners returning to see it still standing, unaware and probably unconcerned that an incarcerated fire crew had saved it. There was satisfaction in knowing that our work was as valuable as that of any other firefighter working the blaze and that the gratitude expressed toward first responders included us.

There are other reasons for prisoners to choose fire camp if given the opportunity. They are often located in secluded natural settings, giving inmates the chance to live in an environment that doesn't remotely resemble a prison. There are no walls, and sometimes there aren't even fences. Gun towers are conspicuously absent, and the guards aren't even armed.... [C]onsider the guy pushing a broom in his cell block making the equivalent of one Top Ramen noodle packet per day, just so he can have the privilege of making a collect call to his mother. Or think of the man scrubbing the streaks out of the guards' toilets, making seven cents an hour, half of which goes to pay court fees and restitution, just so he can have those couple of hours outside his cage for the day...

So, while we may have faced the heat of a wildfire for a few bucks a day, and we may have saved a few homes and been happy doing so, understand that we were rational actors. We wanted to be there, where some of our dignity was returned to us.

Social Networks

TikTok, Facing a US Ban, Is Also Waging Legal Battles Around the World (msn.com) 38

An anonymous reader shared this report from the New York Times: Russia fined TikTok for not removing prohibited content. The results of a presidential election in Romania were thrown out over concerns the app had been used to spread foreign influence. Albania banned TikTok for a year following the stabbing death of a teenager by another one after the two quarreled online... That was all in just the last month...

TikTok has confronted legal and political scrutiny around the world in recent years, facing outright or partial bans in at least 20 countries, as governments have grown alarmed by its ties to China and its wide influence, especially among young people... [A]s TikTok's algorithm captured attention spans around the world, it alarmed lawmakers, who say TikTok has quickly turned from a domain of cat videos and dance trends into a potentially disruptive social, political and economic force. Officials from Montana to New Zealand have warned that TikTok could be used to incite violence, spread false information and worsen mental health. Lawmakers also worry TikTok could share user data like location and browsing history with the Chinese government. Young people need to be protected from "the frightening pitfalls of the algorithm," [Albania prime minister Edi] Rama said.

TikTok lost its largest audience (India) "after India's simmering geopolitical conflict with China boiled over into hand-to-hand combat along their shared border" — resulting in a total ban in the world's single most-populous country. And the article notes TikTok is also blocked on government devices in Taiwan, Britain, Australia, France, and Canada, "as well as the executive arm of the European Union and New Zealand's Parliament..."

But "Despite the mounting scrutiny, TikTok remains incredibly popular worldwide. More than a billion people use the app every month."
AI

Foreign Cybercriminals Bypassed Microsoft's AI Guardrails, Lawsuit Alleges (arstechnica.com) 3

"Microsoft's Digital Crimes Unit is taking legal action to ensure the safety and integrity of our AI services," according to a Friday blog post by the unit's assistant general counsel. Microsoft blames "a foreign-based threat-actor group" for "tools specifically designed to bypass the safety guardrails of generative AI services, including Microsoft's, to create offensive and harmful content.

Microsoft "is accusing three individuals of running a 'hacking-as-a-service' scheme," reports Ars Technica, "that was designed to allow the creation of harmful and illicit content using the company's platform for AI-generated content" after bypassing Microsoft's AI guardrails: They then compromised the legitimate accounts of paying customers. They combined those two things to create a fee-based platform people could use. Microsoft is also suing seven individuals it says were customers of the service. All 10 defendants were named John Doe because Microsoft doesn't know their identity.... The three people who ran the service allegedly compromised the accounts of legitimate Microsoft customers and sold access to the accounts through a now-shuttered site... The service, which ran from last July to September when Microsoft took action to shut it down, included "detailed instructions on how to use these custom tools to generate harmful and illicit content."

The service contained a proxy server that relayed traffic between its customers and the servers providing Microsoft's AI services, the suit alleged. Among other things, the proxy service used undocumented Microsoft network application programming interfaces (APIs) to communicate with the company's Azure computers. The resulting requests were designed to mimic legitimate Azure OpenAPI Service API requests and used compromised API keys to authenticate them. Microsoft didn't say how the legitimate customer accounts were compromised but said hackers have been known to create tools to search code repositories for API keys developers inadvertently included in the apps they create. Microsoft and others have long counseled developers to remove credentials and other sensitive data from code they publish, but the practice is regularly ignored. The company also raised the possibility that the credentials were stolen by people who gained unauthorized access to the networks where they were stored...

The lawsuit alleges the defendants' service violated the Computer Fraud and Abuse Act, the Digital Millennium Copyright Act, the Lanham Act, and the Racketeer Influenced and Corrupt Organizations Act and constitutes wire fraud, access device fraud, common law trespass, and tortious interference.

Social Networks

'What If They Ban TikTok and People Keep Using It Anyway?' (yahoo.com) 101

"What if they ban TikTok and people keep using it anyway?" asks the New York Times, saying a pending ban in America "is vague on how it would be enforced" Some experts say that even if TikTok is actually banned this month or soon, there may be so many legal and technical loopholes that millions of Americans could find ways to keep TikTok'ing. The law is "Swiss cheese with lots of holes in it," said Glenn Gerstell, a former top lawyer at the National Security Agency and a senior adviser at the Center for Strategic and International Studies, a policy research organization. "There are obviously ways around it...." When other countries ban apps, the government typically orders internet providers and mobile carriers to block web traffic to and from the blocked website or app. That's probably not how a ban on TikTok in the United States would work. Two lawyers who reviewed the law said the text as written doesn't appear to order internet and mobile carriers to stop people from using TikTok.

There may not be unanimity on this point. Some lawyers who spoke to Bloomberg News said internet providers would be in legal hot water if they let their customers continue to use a banned TikTok. Alan Rozenshtein, a University of Minnesota associate law professor, said he suspected internet providers aren't obligated to stop TikTok use "because Congress wanted to allow the most dedicated TikTok users to be able to access the app, so as to limit the First Amendment infringement." The law also doesn't order Americans to stop using TikTok if it's banned or to delete the app from our phones....

Odds are that if the Supreme Court declares the TikTok law constitutional and if a ban goes into effect, blacklisting the app from the Apple and Google app stores will be enough to stop most people from using TikTok... If a ban goes into effect and Apple and Google block TikTok from pushing updates to the app on your phone, it may become buggy or broken over time. But no one is quite sure how long it would take for the TikTok app to become unusable or compromised in this situation.

Users could just sideload the app after downloading it outside a phone's official app store, the article points out. (More than 10 million people sideloaded Fortnite within six weeks of its removal from Apple and Google's app stores.) And there's also the option of just using a VPN — or watching TikTok's web site.

(I've never understood why all apps haven't already been replaced with phone-optimized web sites...)
Technology

Automattic Slashes WordPress.org Support in Battle With WP Engine (automattic.com) 41

Automattic is cutting its weekly contributions to WordPress.org from 3,988 hours to 45 hours, escalating tensions with rival WP Engine amid their ongoing legal dispute. The dramatic reduction comes after a federal court granted WP Engine an injunction over Automattic's handling of a disputed plugin.

The company, which runs WordPress.com, blamed the cutback on legal costs from its battle with WP Engine, which CEO Matt Mullenweg previously called a "cancer" to the community. Automattic said remaining contributions will focus on "security and critical updates" through the Five for the Future program.
Bitcoin

DOJ Cleared To Sell $6.5 Billion In Bitcoin Seized From Silk Road (cryptobriefing.com) 71

An anonymous reader quotes a report from Crypto Briefing: The US Department of Justice (DOJ) has been authorized to sell approximately 69,370 Bitcoin seized in connection with the Silk Road darknet marketplace, a haul currently valued at around $6.5 billion, DB News reported Wednesday. The decision is set to end a years-long legal dispute over the BTC stash's ownership. On December 30, a federal judge ruled in favor of the DOJ's request to liquidate the crypto assets, the report said. Battle Born Investments, which had asserted a claim to the Bitcoin stash through a bankruptcy estate, ultimately failed in its bid to delay the sale.

As noted, the group had pursued a Freedom of Information Act (FOIA) request seeking the identity of "Individual X," who initially surrendered Bitcoin, but the effort also proved unsuccessful. Battle Born's legal counsel criticized the DOJ's handling of the case, alleging the department employed "procedural trickery" in its use of civil asset forfeiture to avoid scrutiny. The DOJ, in its arguments before the court, cited Bitcoin's price volatility as motivation for seeking a quick sale of the seized assets. A DOJ spokesperson, when contacted, stated, "The Government will proceed further consistent with the judgment in this case."

The update comes after the US Supreme Court refused to hear an appeal challenging the seizure of the Bitcoin stash, which was brought by Battle Born last October. The decision likely paved the way for the US government to sell Bitcoin, which was valued at $4.4 billion at the time. The US Marshals Service is expected to manage the liquidation process, which, if confirmed, will be one of the largest sales of seized crypto in history.
Further reading: Judge Rejects Man From Retrieving $750 Million of Bitcoin From Landfill
Bitcoin

Judge Rejects Man From Retrieving $750 Million of Bitcoin From Landfill (crypto.news) 127

An IT engineer from Wales lost a decade-long legal battle to recover a hard drive containing 8,000 Bitcoins from a Newport landfill. The hard drive, accidentally thrown away in 2013, is now valued between $700-750 million. crypto.news reports: However, Judge Keyser KC ruled there were no "reasonable grounds" for the claim, citing environmental concerns and the council's ownership of the landfill contents. The landfill reportedly holds 1.4 million tonnes of waste, but Howells claims to have pinpointed the hard drive's location to a 100,000-ton section. Reacting to the ruling, Howells expressed frustration, calling it a "kick in the teeth," according to the BBC.
Facebook

Mark Zuckerberg Gave Meta's Llama Team the OK To Train On Copyright Works, Filing Claims (techcrunch.com) 70

Plaintiffs in Kadrey v. Meta allege that Meta CEO Mark Zuckerberg authorized the team behind the company's Llama AI models to use a dataset of pirated ebooks and articles for training. They further accuse the company of concealing its actions by stripping copyright information and torrenting the data. TechCrunch reports: In newly unredacted documents filed (PDF) with the U.S. District Court for the Northern District of California late Wednesday, plaintiffs in Kadrey v. Meta, who include bestselling authors Sarah Silverman and Ta-Nehisi Coates, recount Meta's testimony from late last year, during which it was revealed that Zuckerberg approved Meta's use of a data set called LibGen for Llama-related training. LibGen, which describes itself as a "links aggregator," provides access to copyrighted works from publishers including Cengage Learning, Macmillan Learning, McGraw Hill, and Pearson Education. LibGen has been sued a number of times, ordered to shut down, and fined tens of millions of dollars for copyright infringement.

According to Meta's testimony, as relayed by plaintiffs' counsel, Zuckerberg cleared the use of LibGen to train at least one of Meta's Llama models despite concerns within Meta's AI exec team and others at the company. The filing quotes Meta employees as referring to LibGen as a "data set we know to be pirated," and flagging that its use "may undermine [Meta's] negotiating position with regulators." The filing also cites a memo to Meta AI decision-makers noting that after "escalation to MZ," Meta's AI team "[was] approved to use LibGen." (MZ, here, is rather obvious shorthand for "Mark Zuckerberg.")

The details seemingly line up with reporting from The New York Times last April, which suggested that Meta cut corners to gather data for its AI. At one point, Meta was hiring contractors in Africa to aggregate summaries of books and considering buying the publisher Simon & Schuster, according to the Times. But the company's execs determined that it would take too long to negotiate licenses and reasoned that fair use was a solid defense. The filing Wednesday contains new accusations, like that Meta might've tried to conceal its alleged infringement by stripping the LibGen data of attribution.

The Courts

Google Faces Trial For Collecting Data On Users Who Opted Out (arstechnica.com) 21

An anonymous reader quotes a report from Ars Technica: A federal judge this week rejected Google's motion to throw out a class-action lawsuit alleging that it invaded the privacy of users who opted out of functionality that records a users' web and app activities. A jury trial is scheduled for August 2025 in US District Court in San Francisco. The lawsuit concerns Google's Web & App Activity (WAA) settings, with the lead plaintiff representing two subclasses of people with Android and non-Android phones who opted out of tracking. "The WAA button is a Google account setting that purports to give users privacy control of Google's data logging of the user's web app and activity, such as a user's searches and activity from other Google services, information associated with the user's activity, and information about the user's location and device," wrote (PDF) US District Judge Richard Seeborg, the chief judge in the Northern District Of California.

Google says that Web & App Activity "saves your activity on Google sites and apps, including associated info like location, to give you faster searches, better recommendations, and more personalized experiences in Maps, Search, and other Google services." Google also has a supplemental Web App and Activity setting that the judge's ruling refers to as "(s)WAA." "The (s)WAA button, which can only be switched on if WAA is also switched on, governs information regarding a user's '[Google] Chrome history and activity from sites, apps, and devices that use Google services.' Disabling WAA also disables the (s)WAA button," Seeborg wrote. But data is still sent to third-party app developers through the Google Analytics for Firebase (GA4F), "a free analytical tool that takes user data from the Firebase kit and provides app developers with insight on app usage and user engagement," the ruling said. GA4F "is integrated in 60 percent of the top apps" and "works by automatically sending to Google a user's ad interactions and certain identifiers regardless of a user's (s)WAA settings, and Google will, in turn, provide analysis of that data back to the app developer."

Plaintiffs have brought claims of privacy invasion under California law. Plaintiffs "present evidence that their data has economic value," and "a reasonable juror could find that Plaintiffs suffered damage or loss because Google profited from the misappropriation of their data," Seeborg wrote. The lawsuit was filed in July 2020. The judge notes that summary judgment can be granted when "there is no genuine dispute as to any material fact and the movant is entitled to judgment as a matter of law." Google hasn't met that standard, he ruled.
In a statement provided to Ars, Google said that "privacy controls have long been built into our service and the allegations here are a deliberate attempt to mischaracterize the way our products work. We will continue to make our case in court against these patently false claims."
Social Networks

TikTok Pushes Users To Lemon8 As Ban Looms (axios.com) 71

TikTok has been pushing the platform's sister app, Lemon8, encouraging users to migrate via sponsored posts amid a looming ban. Axios reports: In the last few weeks, Lemon8 has been promoting its app to TikTok users through sponsored TikTok videos. In one sponsored post, TikTok user @miller.dailylife shares a video with a creator saying, "TikTok actually has another backup app. It's called Lemon8 ... and it automatically signs you in with your TikTok so you can still keep the same TikTok name and things like that. And it's supposed to transfer your followers over. ... Once you add Lemon8, it automatically pops up on your TikTok bio, so that people can just click on it. So, just so you guys know, now that they're trying to do this ban, if you want to have somewhere else to go where the government is not 100% controlling what we see, what we consume ... Just go ahead and go on to Lemon8."

In November, TikTok began informing users of its sister app, Lemon8, that beginning late that month Lemon8 would be powered by TikTok, and their TikTok usernames would also be used on Lemon8. "Some of your data on TikTok will be used to power services on lemon8," the notice says. "Your Lemon8 profile link will be shown to your TikTok profile publicly by default," it continues. "You can choose not to show it by editing your TikTok profile."
Last March, Lemon8 jumped into the U.S. App Store's Top 10 list shortly after it launched in the U.S. It currently ranks as one of the top-ranking free apps on Apple's app store.

The report notes that the TikTok ban law also applies to other apps owned by TikTok's Chinese parent ByteDance, like Lemon8. "ByteDance could be betting that regulators and app store companies are so focused on TikTok that they won't pay attention to its other apps," says Axios.
Government

Big Landlord Settles With US, Will Cooperate In Price-Fixing Investigation (arstechnica.com) 76

An anonymous reader quotes a report from Ars Technica: The US Justice Department today announced it filed an antitrust lawsuit against "six of the nation's largest landlords for participating in algorithmic pricing schemes that harmed renters." One of the landlords, Cortland Management, agreed to a settlement "that requires it to cooperate with the government, stop using its competitors' sensitive data to set rents and stop using the same algorithm as its competitors without a corporate monitor," the DOJ said. The pending settlement requires Cortland to "cooperate fully and truthfully... in any civil investigation or civil litigation the United States brings or has brought" on this subject matter.

The US previously sued RealPage, a software maker accused of helping landlords collectively set prices by giving them access to competitors' nonpublic pricing and occupancy information. The original version of the lawsuit described actions by landlords but did not name any as defendants. The Justice Department filed an amended complaint (PDF) today in order to add the landlords as defendants. The landlord defendants are Greystar, LivCor, Camden, Cushman, Willow Bridge, and Cortland, which collectively "operate more than 1.3 million units in 43 states and the District of Columbia," the DOJ said. "The amended complaint alleges that the six landlords actively participated in a scheme to set their rents using each other's competitively sensitive information through common pricing algorithms," the DOJ said.
The phrase "price fixing" came up in discussions between landlords, the amended complaint said: "For example, in Minnesota, property managers from Cushman & Wakefield, Greystar, and other landlords regularly discussed competitively sensitive topics, including their future pricing. When a property manager from Greystar remarked that another property manager had declined to fully participate due to 'price fixing laws,' the Cushman & Wakefield property manager replied to Greystar, 'Hmm... Price fixing laws huh? That's a new one! Well, I'm happy to keep sharing so ask away. Hoping we can kick these concessions soon or at least only have you guys be the only ones with big concessions! It's so frustrating to have to offer so much.'"

The Justice Department is joined in the case by the attorneys general of California, Colorado, Connecticut, Illinois, Massachusetts, Minnesota, North Carolina, Oregon, Tennessee, and Washington. The case is in US District Court for the Middle District of North Carolina.

Further reading: Are We Entering an AI Price-Fixing Dystopia?
Microsoft

Microsoft Plans $3 Billion AI, Cloud Investment in India (techcrunch.com) 7

Microsoft plans to invest $3 billion to expand its artificial intelligence and cloud Azure services in India, turning to the world's most populous nation to fuel its revenue growth engine. From a report: The firm, which has been operating in India for more than two decades, will also train an additional 10 million people in the country with AI, Microsoft CEO Satya Nadella said at an event in Bengaluru Tuesday.

"The investments in infrastructure and skilling we are announcing today reaffirm our commitment to making India AI-first, and will help ensure people and organizations across the country benefit broadly," said Nadella. "The diffusion rate of AI in India is exciting." India is a key overseas market for American tech giants that have poured tens of billions of dollars in building and scaling their operations in the South Asian market over the past two decades as they work to court businesses serving hundreds of millions of users.

China

Ahead of SCOTUS Hearing, Study Finds TikTok Is Likely Vehicle For Chinese Propaganda (gizmodo.com) 95

A forthcoming peer-reviewed study (PDF) from Rutgers University's Network Contagion Research Institute argues that TikTok surfaces fewer anti-CCP posts compared to Instagram and YouTube, despite higher user engagement with such content. It also found that heavy TikTok usage correlates with more favorable views of China's human rights record. The findings come a Supreme Court hearing later this week on whether the federal government can ban TikTok. Gizmodo reports: The new peer-reviewed paper, which was first reported by The Free Press, begins by examining whether content on TikTok, Instagram, and YouTube related to the keywords "Tiananmen," "Tibet," "Uyghur," and "Xinjiang" tends to display pro- or anti-CCP sentiment. The researchers found that TikTok's algorithm didn't necessarily surface more pro-CCP content in response to searches for those terms, but it delivered fewer anti-CCP posts than did Instagram or YouTube and significantly more posts that were irrelevant to the subject.

In the second stage of their study, the NCRI team tested whether the lower performance of anti-CCP content was a result of less user engagement (likes and comments) with those posts. They found that TikTok users "liked or commented on anti-CCP content nearly four times as much as they liked or commented on pro-CCP content, yet the search algorithm produced nearly three times as much pro-CCP content" while there was no similar discrepancy on Instagram or YouTube.

Finally, the researchers surveyed 1,214 Americans about their social media usage and their views on China's human rights record. The more time users spent on any social media platform, the more likely they were to have favorable views of China's human rights record, the survey showed. Users were particularly more likely to have favorable views if they spent more than three hours a day using TikTok. The researchers wrote that they could not definitively conclude that spending more time on TikTok resulted in more positive views of China, but "taken together, the findings from these three studies raise the distinct possibility that TikTok is a vehicle for CCP propaganda."

The Internet

America Still Has Net Neutrality Laws - In States Like California and New York (yahoo.com) 47

A U.S. Appeals Court ruled this week that net neutrality couldn't be reinstated by America's Federal Communications Commission. But "Despite the dismantling of the FCC's efforts to regulate broadband internet service, state laws in California, New York and elsewhere remain intact," notes the Los Angeles Times: This week's decision by the 6th U.S. Circuit Court of Appeals, striking down the FCC's open internet rules, has little bearing on state laws enacted during the years-long tug-of-war over the government's power to regulate internet service providers, telecommunications experts said. In fact, some suggested that the Cincinnati-based 6th Circuit's decision — along with other rulings and the U.S. Supreme Court's posture on a separate New York case — has effectively fortified state regulators' efforts to fill the gap. "Absent an act of Congress, the FCC has virtually no role in broadband any more," Ernesto Falcon, a program manager for the California Public Utilities Commission, said in an interview. "The result of this decision is that states like California, New York and others will have to govern and regulate broadband carriers on our own."

California has one of the nation's strongest laws on net neutrality, the principle that internet traffic must be treated equally to ensure a free and open network. Former Gov. Jerry Brown signed the measure into law in 2018, months after federal regulators in President elect-Donald Trump's first administration repealed the net neutrality rules put in place under President Obama. Colorado, Oregon and other states also adopted their own standards.

The Golden State's law has already survived legal challenges. It also prompted changes in the way internet service providers offered plans and services. "California's net neutrality law, which is seen as the gold standard by consumer advocates, carries national impact," Falcon said.... "The state's authority and role in broadband access has grown dramatically now," Falcon said.

California's net neutrality rules prohibit "throttling" data speeds, according to the article.
China

Are US Computer Networks A 'Key Battlefield' in any Future Conflict with China? (msn.com) 72

In a potential U.S.-China conflict, cyberattackers are military weapons. That's the thrust of a new article from the Wall Street Journal: The message from President Biden's national security adviser was startling. Chinese hackers had gained the ability to shut down dozens of U.S. ports, power grids and other infrastructure targets at will, Jake Sullivan told telecommunications and technology executives at a secret meeting at the White House in the fall of 2023, according to people familiar with it. The attack could threaten lives, and the government needed the companies' help to root out the intruders.

What no one at the briefing knew, including Sullivan: China's hackers were already working their way deep inside U.S. telecom networks, too. The two massive hacking operations have upended the West's understanding of what Beijing wants, while revealing the astonishing skill level and stealth of its keyboard warriors — once seen as the cyber equivalent of noisy, drunken burglars. China's hackers were once thought to be interested chiefly in business secrets and huge sets of private consumer data. But the latest hacks make clear they are now soldiers on the front lines of potential geopolitical conflict between the U.S. and China, in which cyberwarfare tools are expected to be powerful weapons. U.S. computer networks are a "key battlefield in any future conflict" with China, said Brandon Wales, a former top U.S. cybersecurity official at the Department of Homeland Security, who closely tracked China's hacking operations against American infrastructure. He said prepositioning and intelligence collection by the hackers "are designed to ensure they prevail by keeping the U.S. from projecting power, and inducing chaos at home."

As China increasingly threatens Taiwan, working toward what Western intelligence officials see as a target of being ready to invade by 2027, the U.S. could be pulled into the fray as the island's most important backer... Top U.S. officials in both parties have warned that China is the greatest danger to American security.

In the infrastructure attacks, which began at least as early as 2019 and are still taking place, hackers connected to China's military embedded themselves in arenas that spies usually ignored, including a water utility in Hawaii, a port in Houston and an oil-and-gas processing facility. Investigators, both at the Federal Bureau of Investigation and in the private sector, found the hackers lurked, sometimes for years, periodically testing access. At a regional airport, investigators found the hackers had secured access, and then returned every six months to make sure they could still get in. Hackers spent at least nine months in the network of a water-treatment system, moving into an adjacent server to study the operations of the plant. At a utility in Los Angeles, the hackers searched for material about how the utility would respond in the event of an emergency or crisis. The precise location and other details of the infrastructure victims are closely guarded secrets, and couldn't be fully determined.

American security officials said they believe the infrastructure intrusions — carried out by a group dubbed Volt Typhoon — are at least in part aimed at disrupting Pacific military supply lines and otherwise impeding America's ability to respond to a future conflict with China, including over a potential invasion of Taiwan... The focus on Guam and West Coast targets suggested to many senior national-security officials across several Biden administration agencies that the hackers were focused on Taiwan, and doing everything they could to slow a U.S. response in a potential Chinese invasion, buying Beijing precious days to complete a takeover even before U.S. support could arrive.

The telecom breachers "were also able to swipe from Verizon and AT&T a list of individuals the U.S. government was surveilling in recent months under court order, which included suspected Chinese agents. The intruders used known software flaws that had been publicly warned about but hadn't been patched."

And ultimately nine U.S. telecoms were breached, according to America's deputy national security adviser for cybersecurity — including what appears to have been a preventable breach at AT&T (according to "one personal familiar with the matter"): [T]hey took control of a high-level network management account that wasn't protected by multifactor authentication, a basic safeguard. That granted them access to more than 100,000 routers from which they could further their attack — a serious lapse that may have allowed the hackers to copy traffic back to China and delete their own digital tracks.
The details of the various breaches are stunning: Chinese hackers gained a foothold in the digital underpinnings of one of America's largest ports in just 31 seconds. At the Port of Houston, an intruder acting like an engineer from one of the port's software vendors entered a server designed to let employees reset their passwords from home. The hackers managed to download an encrypted set of passwords from all the port's staff before the port recognized the threat and cut off the password server from its network...
Government

US Sanctions Chinese Firm Linked to Seized Botnet (msn.com) 6

Remember that massive botnet run by Chinese government hackers? Flax Typhoon "compromised computer networks in North America, Europe, Africa, and across Asia, with a particular focus on Taiwan," according to the U.S. Treasury Department. (The group's botnet breaching this autumn affected "at least 260,000 internet-connected devices," reports the Washington Post, "roughly half of which were located in the United States.")

Friday America's Treasury Department sanctioned "a Beijing-based cybersecurity company for its role in multiple computer intrusion incidents against U.S. victims..." according to an announcement from the department's Office of Foreign Assets Control. "Between summer 2022 and fall 2023, Flax Typhoon actors used infrastructure tied to Integrity Tech during their computer network exploitation activities against multiple victims. During that time, Flax Typhoon routinely sent and received information from Integrity Tech infrastructure."

From the Washington Post: The group behind the attacks was active since at least 2021, but U.S. authorities only managed to wrest control of the devices from the hackers in September, after the FBI won a court order that allowed the agency to send commands to the infected devices...

Treasury's designation follows sanctions announced last month on Sichuan Silence Information Technology Company, in which U.S. officials accused the company of exploiting technology flaws to install malware in more than 80,000 firewalls, including those protecting U.S. critical infrastructure. The new sanctions on Beijing Integrity Technology are notable due to the company's public profile and outsize role in servicing China's police and intelligence services via state-run hacking competitions. The company, which is listed in Shanghai and has a market capitalization of more than $327 million, plays a central role in providing state agencies "cyber ranges" — technology that allows them to simulate cyberattacks and defenses...

In September, FBI Director Christopher A. Wray said the Flax Typhoon attack successfully infiltrated universities, media organizations, corporations and government agencies, and in some cases caused significant financial losses as groups raced to replace the infected hardware. He said at the time that the operation to shut down the network was "one round in a much longer fight...." A 2024 assessment by the Office of the Director of National Intelligence said China is the most "active and persistent" cyberthreat and that actors under Beijing's direction have made efforts to breach U.S. critical infrastructure with the intention of lying in wait to be able to launch attacks in the event of major conflict.

"The Treasury sanctions bar Beijing Integrity Technology from access to U.S. financial systems and freeze any assets the company might hold in the United States," according to the article, "but the moves are unlikely to have a significant effect on the company," (according to Dakota Cary, a fellow at the Atlantic Council who has studied the company's role in state-sponsored hacking).

Slashdot Top Deals